Phishing simulation: test how your employees respond
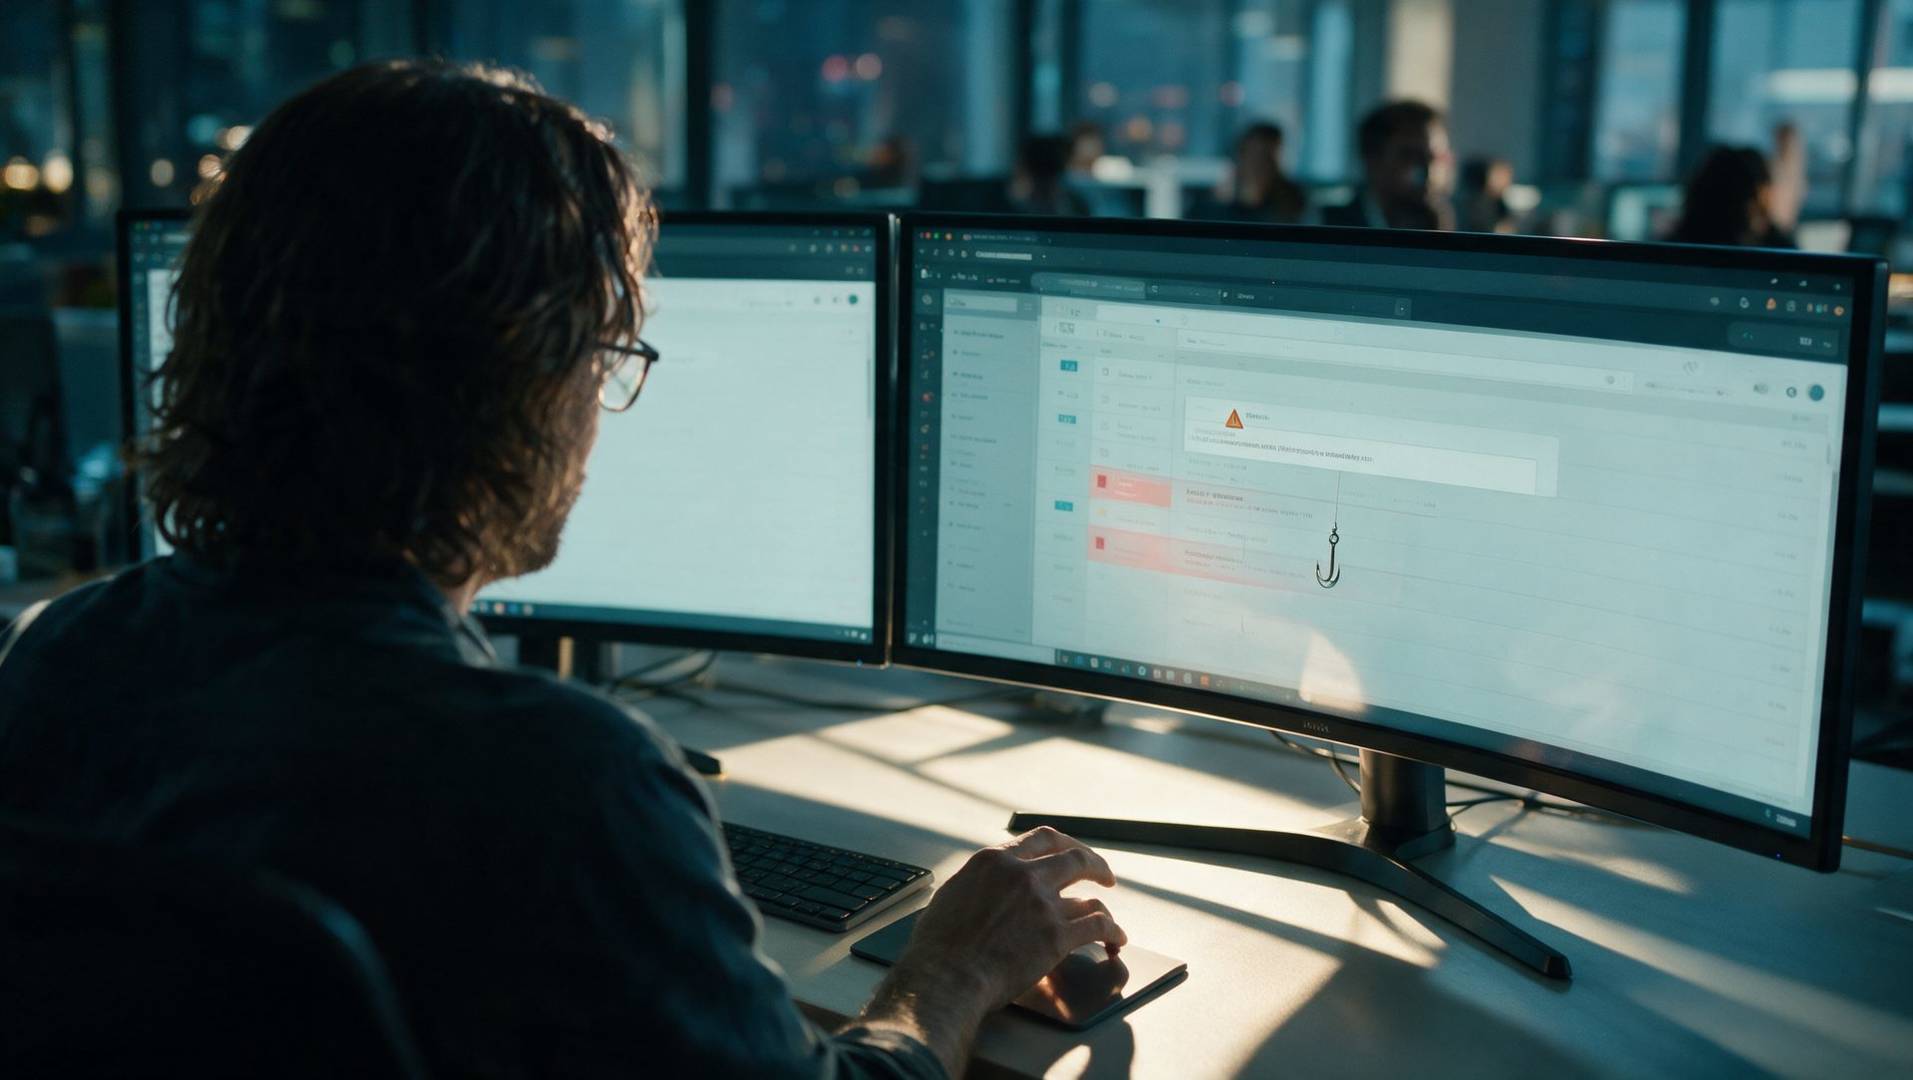
One convincing phishing email is enough for an attacker to get in. With a phishing simulation by Secure Sense, you measure safely and in a controlled way how your employees respond: who opens it, who clicks, who enters data and who reports the email. No theory but your own numbers, as a starting point to get better at this together.
How does the phishing simulation work?
Step 1: Tailored scenario. Together we design a realistic campaign that fits your organization, from a generic email to a targeted variant.
Step 2: Controlled sending. The email goes to one department or the whole organization, at a moment we choose together.
Step 3: Measurement. We record the entire course of events: opened, clicked, data entered and reported as phishing, plotted on a timeline.
Also read about the Microsoft 365 security audit and the frequently asked questions.
Step 4: Report and follow-up. You receive a clear report with the numbers and concrete recommendations, and together we discuss how to raise awareness in a structural way. Optional: an analysis of the passwords that were entered (not included in the report by default for privacy reasons) and technical and organizational recommendations based on the results.
Respect for your people
A phishing simulation is meant to learn from, not to name and shame employees. We report at the organization and department level and advise you on careful internal communication, so that the result builds support instead of distrust.
Workshop and e-learning as follow-up
After the simulation you know where you stand. If you wish, a tailored workshop or e-learning follows to raise security awareness in a structural way, with a repeat measurement to demonstrate the progress. Awareness is not a one-time project. A fixed rhythm of measuring and training works best.
Frequently asked questions
Are we allowed to test our employees like this?
As an employer, you may test the resilience of your organization. There are points to consider, such as coordination with a works council if you have one and handling the results with care. We advise you on this during the preparation.
How often is a phishing test useful?
As a baseline measurement before a training program, and then periodically to measure the effect.
Can we combine this with a penetration test (pentest)?
Yes, that happens often: technology and people in a single picture.
Want to know how your organization responds to a real phishing attack? Request a no-obligation quote.