Web application pentest
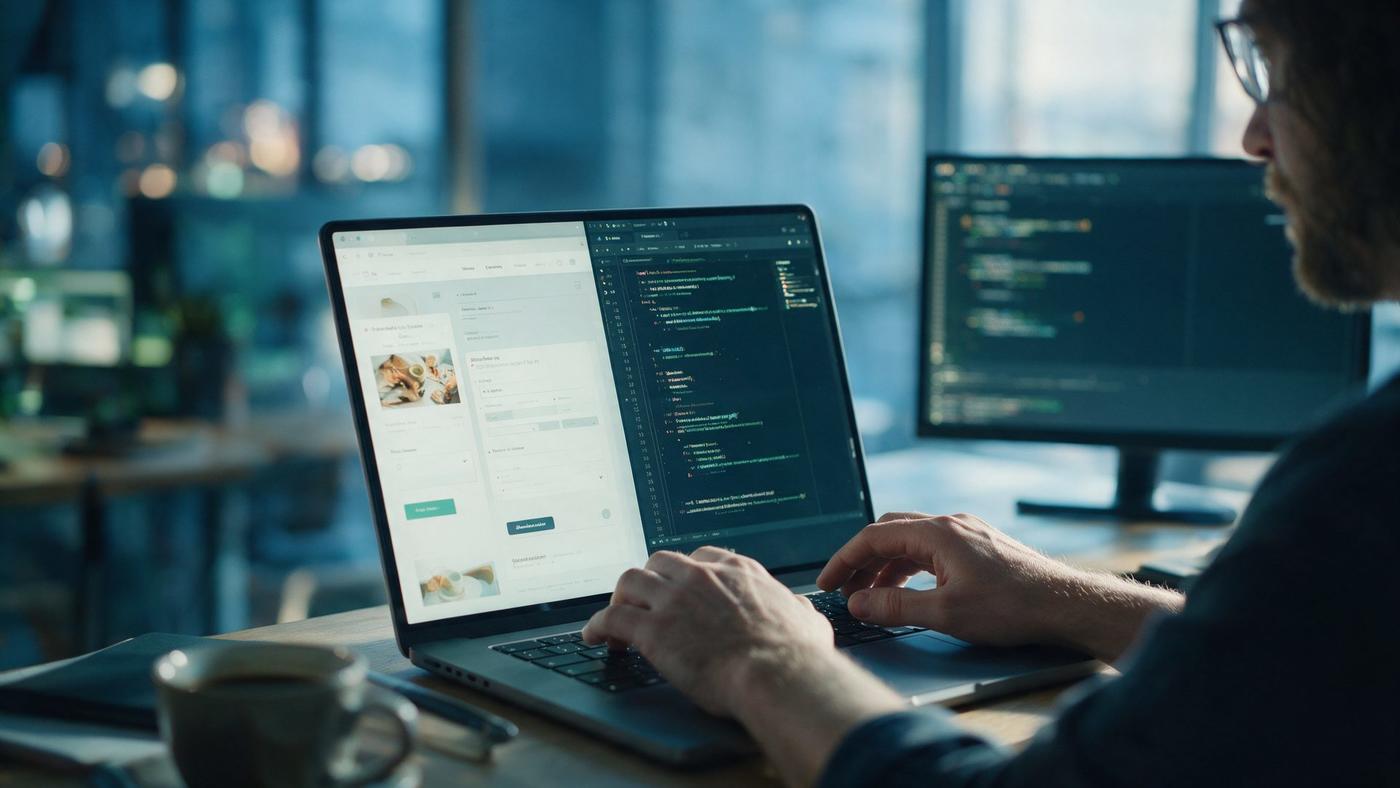
In a web application penetration test (pentest), a specialist examines your website, online store, portal, SaaS application or API for vulnerabilities that an attacker can exploit. Manual testing, based on the OWASP Top 10 and other standards, with proof for every finding. That way you know for sure that customer data, orders and business information are not up for grabs.
What do we test?
Among other things, we test:
- Injection attacks, such as SQL injection, which let attackers steal or manipulate data
- Authentication and session management: login, password reset, two-factor authentication, sessions that never expire
- Access control: can user A see the data of user B, or can a regular user reach admin functions?
- Flaws in the business logic, such as price manipulation in an ordering process or skipping steps
- Insecure configurations, outdated components and known vulnerabilities
- APIs and integrations with other systems, including the endpoints that "nobody knows about"
- File uploads, export functions and other places where data enters and leaves the application
Who is this pentest for?
For every organization whose web application holds something of value: an online store with customer and payment data, a SaaS product with your customers' business data, a portal where clients log in, or a custom application that an agency built for you. Is your software developed by an external party? Then an independent test is especially valuable: we have no stake in the outcome.
With or without prior knowledge
We perform most web application pentests as a gray box test: you give us one or more test accounts and we test what an outsider and what a logged-in user can reach. A black box test (without any prior knowledge) or a white box test (with full knowledge of the application) is also possible. During the intake we advise what fits your goal.
Optional: secure code review
Do you want more certainty than a test from the outside can give? Then we combine the pentest with a review of the source code. Vulnerabilities that are visible in the code but hard to find from the outside still come to light this way. Especially valuable for software vendors and applications with sensitive data.
What do you get?
A report with a management summary in plain language and a technical section that gives the risk rating, the proof with steps to reproduce and clear remediation advice for every finding. We walk you through the report in person, together with your developer or agency if you wish, and on request we verify with a retest that everything has been fixed properly.
Frequently asked questions
Can the test disrupt our production environment?
We test with care and agree on risky actions with you in advance. Testing on a staging environment is also possible. We discuss this during the intake.
How long does a web application pentest take?
That depends on the size and complexity of the application. For an average web application, 16 to 40 hours of testing is common. After the intake you know exactly.
Does our hosting provider need to give permission?
Often, yes. We know what hosting providers need and help you arrange this quickly.
Also read which factors determine the price of a pentest and how our approach works from intake to retest.
Do you want to know what an attacker can do in your application? Request a no-obligation quote.
- Prevention is better than cure
- Insight into your weak spots and vulnerabilities
- Discretion guaranteed
- Clear and well-organized reporting
- Less risk of data breaches, reputational or financial damage